

Creating a User and Granting IoTDA Permissions
You can use Identity and Access Management for fine-grained permissions control of your IoTDA resources. With IAM, you can:
- Create IAM users for personnel based on your enterprise's organizational structure. Each IAM user has their own identity credentials for accessing IoTDA resources.
- Grant users only the permissions required to perform a given task based on their job responsibilities.
- Entrust a Huawei Cloud account or a cloud service to perform efficient O&M on your IoTDA resources.
If your Huawei Cloud account does not need individual IAM users, then you may skip this section.
This section describes the procedure for granting permissions. Figure 1 shows the process flow.
Prerequisites
Before granting permissions to user groups, learn about system-defined permissions supported by IoTDA. To grant permissions for other services, learn about all system-defined permissions supported by IAM by referring to System-defined Permissions.
Process
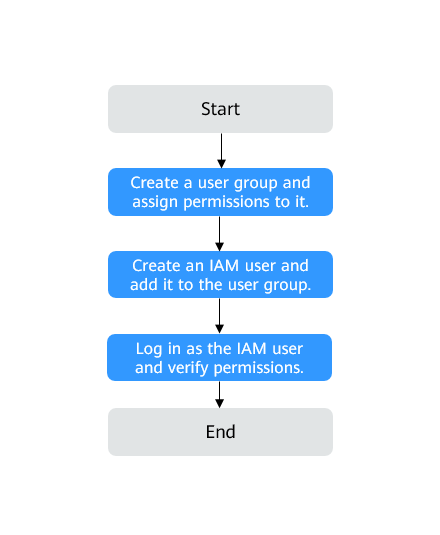
- Create a user group and assign permissions: Create a user group on the IAM console and assign IoTDA permissions to the group, for example, IoTDA ReadOnlyAccess.
- Create a user and add it to the user group: Create a user on the IAM console and add the user to the group created in 1.
- Log in as an IAM user: Log in to the console as the created user, switch to the authorized region, and verify permissions.
- Choose Service List > IoT Device Access. Then attempt to register a device on the IoTDA console. If a message appears, indicating that you have insufficient permissions to perform the operation, the IoTDA ReadOnlyAccess policy is in effect.
- Choose another service from Service List. If a message appears, indicating that you have insufficient permissions to access the service, the IoTDA ReadOnlyAccess policy is in effect.
What is your overall rating for this page?
Thank you very much for your feedback. We will continue working to improve the documentation.See the reply and handling status in My Cloud VOC.
For any further questions, feel free to contact us through the chatbot.
Chatbot


