

Updated on 2026-08-29 GMT+08:00
Collecting Audit Logs
CCE allows you to collect the logs of master nodes. On the Logging page, choose Kubernetes Audit Logs and determine whether to report Kubernetes audit logs to LTS.
Constraints
- The cluster version must be v1.21.7-r0 or later, v1.23.5-r0 or later, or 1.25.
- The LTS resource quota must be sufficient.
Audit Logs
| Log Type | Component | Log Stream | Description |
|---|---|---|---|
| Kubernetes audit logs | audit | audit-{{clusterID}} | An audit log is a chronological record of user operations on Kubernetes APIs and control plane activities for security. |
Enabling Kubernetes Audit Logging for a Cluster
Enabling Audit Logging During Cluster Creation
- Log in to the CCE console.
- Click Buy Cluster. Configure the parameters and click Next: Select Add-on.
- On the displayed page, select Cloud Native Log Collection and click Next: Configure Add-on.
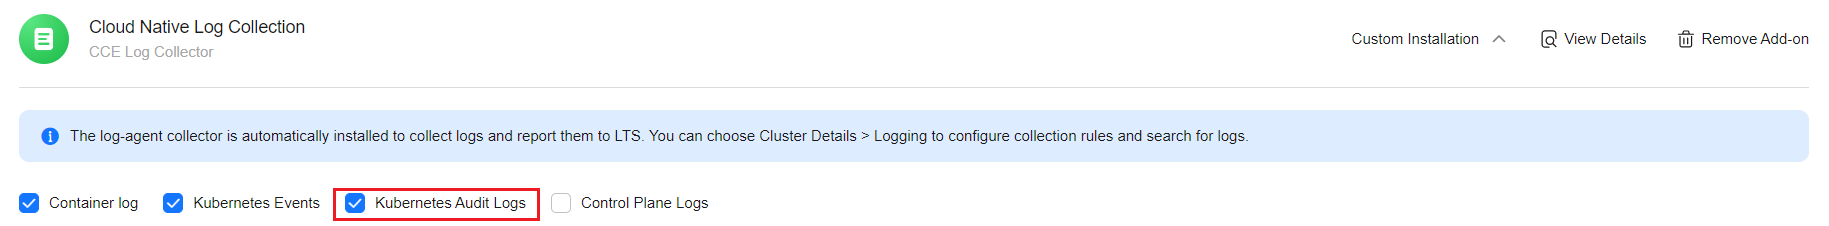
- On the displayed page, select Kubernetes Audit Logs for Cloud Native Log Collection. Figure 1 Enabling audit logging during cluster creation
- Click Next: Confirm Settings.
Enabling Audit Logging for an Existing Cluster
- Log in to the CCE console and click the cluster name to access the cluster console.
- In the navigation pane, choose Logging.
- Click the Kubernetes Audit Logs tab, select the audit component, and click Enable. Figure 2 Enabling audit logging for an existing cluster

Viewing Kubernetes Audit Logs of a Cluster
Viewing Kubernetes Audit Logs of the Target Cluster on the CCE Console
- Log in to the CCE console and click the cluster name to access the cluster console.
- In the navigation pane, choose Logging.
- Click the Kubernetes Audit Logs tab to view the audit logs of the cluster. Figure 3 Viewing Kubernetes Audit Logs of the Target Cluster on the CCE Console

Viewing Kubernetes Audit Logs of the Target Cluster on the LTS Console
- Log in to the LTS console and choose Log Management.
- Search for the log group by cluster ID and click the log group name to view the log streams. Figure 4 Viewing Kubernetes audit logs on the LTS console

Disabling Kubernetes Audit Logging
- Log in to the CCE console and click the cluster name to access the cluster console.
- In the navigation pane, choose Logging.
- Click the Kubernetes Audit Logs tab. Click Configure Control Plane Audit Logging in the upper right corner and determine whether to enable control plane audit logging. Figure 5 Disabling audit logging

- Deselect audit and click OK.
After you disable audit logging, logs are no longer written to the original log stream, but the existing logs will not be deleted and expenditures may be incurred for this.
What is your overall rating for this page?
0
1
2
3
4
5
6
7
8
9
10
Very dissatisfiedVery satisfied
Thank you very much for your feedback. We will continue working to improve the documentation.
The system is busy. Please try again later.


