Configuring SNI for a LoadBalancer Service
An SNI certificate is an extended server certificate that allows the same IP address and port number to provide multiple access domain names for external systems. Different security certificates can be used based on the domain names requested by clients to ensure HTTPS communication security.
When configuring SNI, you need to add a certificate associated with a domain name. The client submits the requested domain name information when initiating an SSL handshake request. After receiving the SSL request, the load balancer searches for the certificate based on the domain name. If the certificate is found, the load balancer will return it to the client. If the certificate is not found, the load balancer will return the default server certificate.
After SNI is configured, if you delete the SNI configuration on the CCE console or delete the target annotation from the YAML file, the configuration on the ELB will be retained.
Prerequisites
- A Kubernetes cluster is available and the cluster version meets the following requirements:
- v1.23: v1.23.13-r0 or later
- v1.25: v1.25.8-r0 or later
- v1.27: v1.27.5-r0 or later
- v1.28: v1.28.3-r0 or later
- Other clusters of later versions
- You have created one or more SNI certificates in ELB and specified a domain name in these certificates.
- To create a cluster using commands, ensure kubectl is used. For details, see Accessing a Cluster Using kubectl.
Step 1: Deploy a Sample Application
This section uses a Nginx Deployment as an example.
- Log in to the CCE console and click the cluster name to access the cluster console.
- In the navigation pane, choose Workloads. In the upper right corner, click Create Workload.
- In the Basic Info area, enter the workload name. In this example, the workload name is nginx. Retain the default settings for other parameters.
- In Container Information under Container Settings, specify the image name and tag. Retain the default settings for other parameters.
Parameter
Example
Image Name
Click Select Image. In the displayed dialog box, search for nginx, select it, and click OK.
Image Tag
Select the latest image tag.
- Retain the default settings for other parameters and click Create Workload.
Step 2: Create a LoadBalancer Service and Configure SNI
Use one of the following methods.
This section uses the certificates cert-test and cert-sni-test as an example, where cert-sni-test includes an SNI domain name. Replace these certificates as needed.
- Log in to the CCE console and click the cluster name to access the cluster console.
- In the navigation pane, choose Services and Ingresses. In the upper right corner, click Create Service.
In this example, only mandatory parameters for configuring SNI are listed. Retain the default settings for other parameters. For details, see Using the CCE Console.
- Configure basic parameters.
Parameter
Description
Example
Service Type
Select LoadBalancer.
None
Service Name
Enter a name, which can be the same as the workload name.
nginx
Namespace
Select the namespace that the workload belongs to.
default
Selector
Add the key and value of a pod label. The Service will be associated with the workload pods based on the label and direct traffic to the pods with this label.
You can also click Reference Workload Label to use the label of an existing workload. In the dialog box displayed, select a workload and click OK.
app:nginx

- Configure load balancer parameters.
Parameter
Description
Example
Load Balancer
Select a load balance type and how the load balancer will be created. To enable HTTP/HTTPS on the listener port of a dedicated load balancer, the type of the load balancer must be Application (HTTP/HTTPS) or Network (TCP/UDP/TLS) & Application (HTTP/HTTPS).- Use existing: Only the load balancers in the same VPC as the cluster can be selected. If no load balancer is available, click Create Load Balancer to create one on the ELB console.
- Auto create: The load balancer will be created in the VPC that the cluster belongs to. For details, see Table 1.
An existing Dedicated load balancer of the Network (TCP/UDP/TLS) & Application (HTTP/HTTPS) type

- Configure access parameters.
Parameter
Description
Example
Service Affinity
Whether to route external traffic to a local node or a cluster-wide endpoint. For details, see Service Affinity (externalTrafficPolicy).- Cluster-level: The IP addresses and ports of all nodes in a cluster can access the workload associated with the Service. However, accessing the Service may result in performance deterioration due to route redirection, and the client's source IP address may not be obtainable.
- Node-level: Only the IP address and port of the node where the workload is located can access the workload associated with the Service. Accessing the Service will not result in a performance deterioration due to route redirection, and the client's source IP address can be obtained.
Cluster-level
Port
- Protocol: the protocol used by the Service.
- Container Port: the port that the workload listens on. For example, Nginx uses port 80 by default.
- Service Port: the port used by the Service.
- Listen on a port: The port ranges from 1 to 65535.
- Listen on ports: ELB allows you to create listeners that listen on ports within specified ranges. Each listener can support up to 10 non-overlapping port ranges.
To configure port ranges for load balancer listeners, ensure the following conditions are met:
- The cluster version must be v1.23.18-r0, v1.25.13-r0, v1.27.10-r0, v1.28.8-r0, v1.29.4-r0, v1.30.1-r0, or later.
- A dedicated load balancer must be used with TCP/UDP selected.
- This function requires ELB. Before using this function, check whether ELB supports full-port listening and forwarding for layer-4 protocols in the current region.
- Frontend Protocol: Set the protocol of the load balancer listener for establishing connections with clients. When a dedicated load balancer is selected, HTTP/HTTPS can be configured only when Application (HTTP/HTTPS) is selected.
NOTE:When a LoadBalancer Service is created, a random node port number (NodePort) is automatically generated.
- Protocol: TCP
- Container Port: 80
- Service Port: 443
- Frontend Protocol: HTTPS

- Configure listener HTTP/HTTPS and SNI parameters.
Parameter
Description
Constraint
Example
SSL Authentication
- One-way authentication: Only the backend server is authenticated. If you also need to authenticate the identity of the client, select two-way authentication.
- Two-way authentication: Both the clients and the load balancer authenticate each other. This ensures only authenticated clients can access the load balancer. No additional backend server configuration is required if you select this option.
This parameter is available only when Frontend Protocol is set to HTTPS or TLS.
Dedicated load balancers are available in clusters v1.23.14-r0, v1.25.9-r0, v1.28.4-r0, or later. Shared load balancers are available in clusters v1.28.15-r60, v1.29.15-r20, v1.30.14-r20, v1.31.10-r20, v1.32.6-r20, v1.33.5-r10, or later.
One-way authentication
CA Certificate
If SSL Authentication is set to Two-way authentication, add a CA certificate to authenticate the client. A CA certificate is issued by a Certificate Authority (CA) and is used to verify the issuer of the client's certificate. If HTTPS two-way authentication is enabled, HTTPS connections can be established only if the client provides a certificate issued by a specific CA.
This parameter is available only when Frontend Protocol is set to HTTPS or TLS and SSL Authentication is set to Two-way authentication.
None
Server Certificate
Select a server certificate.
This parameter is available only when Frontend Protocol is set to HTTPS or TLS.
cert-test
SNI
Determine whether to add an SNI certificate. If an SNI certificate is required, the certificate must contain a domain name.
If the server cannot find an SNI certificate matching the client-requested domain name, it will return the default server certificate.
This parameter is available only when Frontend Protocol is set to HTTPS or TLS.
cert-sni-test

- Configure a backend routing policy.
Parameter
Description
Constraint
Example Value
Backend Protocol
Protocol used by the load balancer to forward requests to backend servers. Backend servers must listen on this protocol and respond to requests.
If Frontend Protocol is set to HTTPS, the backend protocol can be HTTP or HTTPS. The default value is HTTP.
NOTE:When multiple ports are added, if the frontend protocols of some ports are not HTTPS, this configuration takes effect only for HTTPS ports.
This parameter is only available in clusters v1.23.14-r0, v1.25.9-r0, v1.27.6-r0, v1.28.4-r0, or later.
HTTP
- Click Create.
apiVersion: v1
kind: Service
metadata:
  name: test
  labels:
    app: test
  namespace: default
  annotations:
    kubernetes.io/elb.class: performance        # Load balancer type
    kubernetes.io/elb.id: 65318265-4f01-4541-a654-fa74e439dfd3  # ID of an existing load balancer
    kubernetes.io/elb.protocol-port: https:80    # Port where SNI is to be enabled
    kubernetes.io/elb.cert-id: b64ab636f1614e1a960b5249c497a880    # HTTPS server certificate
    kubernetes.io/elb.tls-certificate-ids: 5196aa70b0f143189e4cb54991ba2286,8125d71fcc124aabbe007610cba42d60    # SNI certificate IDs
    kubernetes.io/elb.lb-algorithm: ROUND_ROBIN
spec:
  selector:
    app: test
  externalTrafficPolicy: Cluster
  ports:
    - name: cce-service-0
      targetPort: 80
      nodePort: 0
      port: 80
      protocol: TCP
  type: LoadBalancer
loadBalancerIP: **.**.**.** # Private IP address of the load balancer | Parameter | Type | Description |
|---|---|---|
| kubernetes.io/elb.protocol-port | String | If a Service is HTTP/HTTPS-compliant, configure the protocol and port number in the format of "protocol:port". where,
For example, to use SNI, the Service protocol must be https and the Service port must be 80. Therefore, the parameter value is https:80. |
| kubernetes.io/elb.cert-id | String | ID of an ELB certificate, which is used as the HTTPS server certificate. How to obtain: Log in to the ELB console and choose Certificates. In the certificate list, copy the ID under the target certificate name. |
| kubernetes.io/elb.tls-certificate-ids | String | In ELB, the IDs of SNI certificates that must contain a domain name are separated by commas (,). If the server cannot find an SNI certificate matching the client-requested domain name, it will return the default server certificate. How to obtain: Log in to the ELB console and choose Certificates. In the certificate list, copy the ID under the target certificate name. |
| kubernetes.io/elb.client-ca-cert-id | String | Required only for mutual authentication. The ELB certificate ID serves as the CA certificate. How to obtain: Log in to the ELB console and choose Certificates. In the certificate list, copy the ID under the target certificate name. Dedicated load balancers are available in clusters v1.23.14-r0, v1.25.9-r0, v1.27.6-r0, v1.28.4-r0, or later. Shared load balancers are available in clusters v1.28.15-r60, v1.29.15-r20, v1.30.14-r20, v1.31.10-r20, v1.32.6-r20, v1.33.5-r10, or later. |
Step 3: Access the Workload
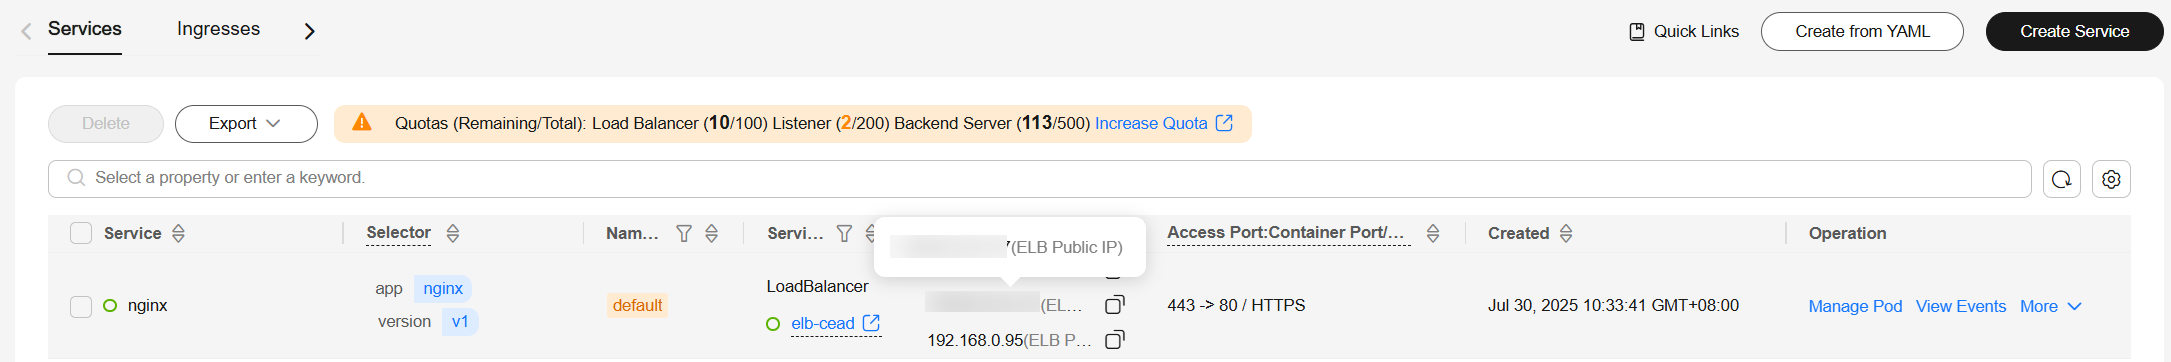
- After the Service is created, copy the load balancer's EIP.
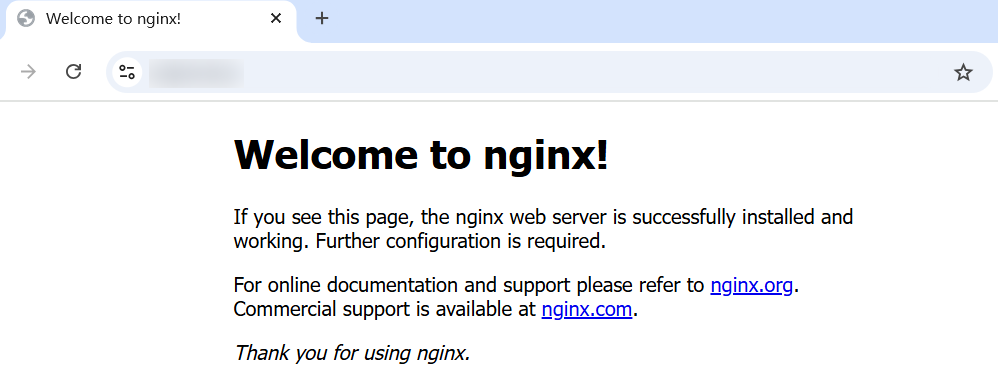
- Configure DNS for a domain name so that you can use the SNI domain name for browser access.
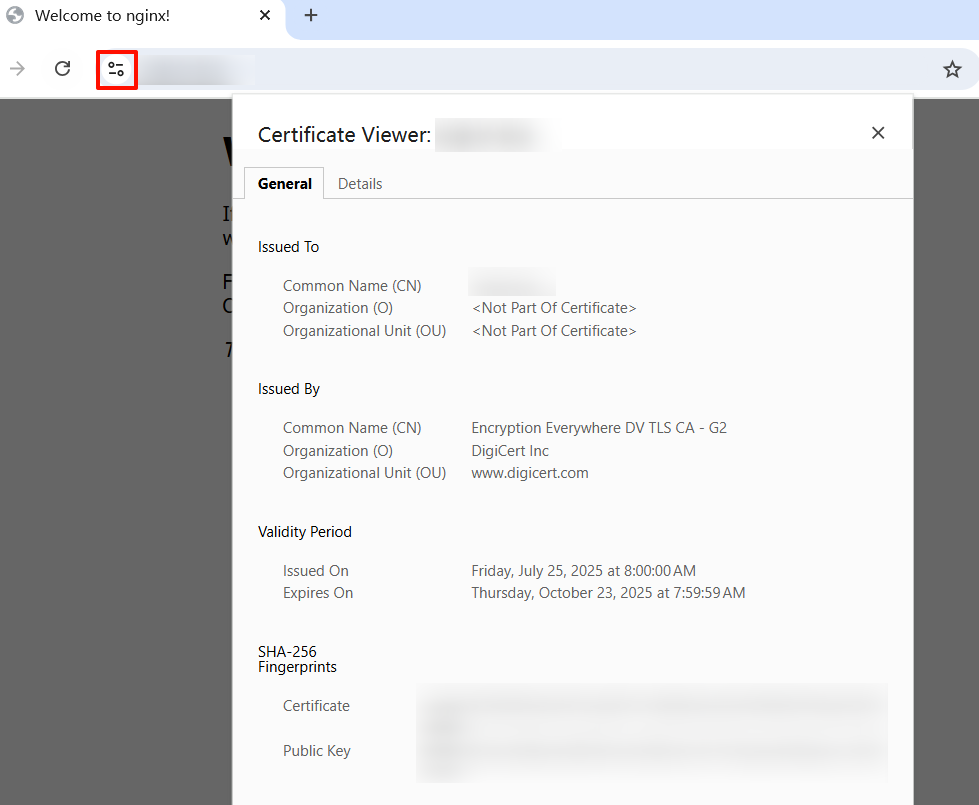
- View the certificate details returned by the server, such as the issuer, validity period, and SHA-256 fingerprint, in the browser to ensure that the certificate corresponds to the requested SNI domain name.