

Authorizing SecMaster
Scenarios
SecMaster depends on some other cloud services. To better use SecMaster, you can authorize SecMaster to perform some operations on some cloud services on your behalf. For example, you can allow SecMaster to execute scheduling tasks and manage resources.
Your authorization is required first time you try to use SecMaster. The following table lists the permissions you need to assign to SecMaster.
| Permission | Description | Principal | Usage |
|---|---|---|---|
| SecMasterBasicEntrustGlobalPolicy | SecMaster global basic agency permissions | SecMaster_Agency | It is a global agency policy used in SecMaster authorization. The core purpose is to delegate the operation permissions of related cloud services to SecMaster. In this way, SecMaster can access and perform operations on other cloud service resources on your behalf, for example, scheduling tasks and maintaining resources. |
| SecMasterBasicEntrustRegionPolicy | SecMaster regional basic agency permissions | SecMaster_Agency | It is a region-level agency policy used in SecMaster authorization. The core purpose is to delegate the operation permissions of related cloud services to SecMaster within a specified region. In this way, SecMaster can access and perform operations on other cloud service resources in the region on your behalf, for example, scheduling tasks and maintaining resources. |
| Tenant Guest | Read-only permissions for all cloud services except IAM | SecMaster_Agency | It is used to query resource information of cloud services except IAM in the baseline check scenario. |
Prerequisites
- The IAM account has been authorized. For details, see How Do I Grant Permissions to an IAM User?
- You have purchased SecMaster.
Authorizing SecMaster
- Log in to the SecMaster console.
- Click
 in the upper left corner of the management console and select a region or project.
- In the navigation pane on the left, choose Workspaces > Management. Figure 1 Workspaces > Management

- (Optional) In the upper part of the workspace management page, click Entrusted Service Authorization - Current Tenant.
The service authorization page is automatically displayed the first time you log in. For details about the authorized permissions, see Table 1. If you have already granted SecMasterBasicEntrustRegionPolicy when purchasing SecMaster, the permissions to be granted here will only include SecMasterBasicEntrustGlobalPolicy and Tenant Guest.
- On the page for assigning permissions, select all required permissions (which are selected by default), select Agree to authorize, and click Confirm.
Authorization by Organization
SecMaster allows you to grant permissions to an organization in just a few clicks. After the permissions are granted, all users in the organization can use the SecMaster service.
- What is the Organizations service?
The Organizations service helps you govern multiple accounts within your organization. It enables you to consolidate multiple accounts into a created organization so that you can centrally manage these accounts. You can use Organizations to apply access policies to different accounts in your organization. This helps you better meet the security and compliance requirements of your business. Before you start, make sure you understand Basic Concepts of Organizations.
- Main functions of the Organizations service
The Organizations service provides the following functions:
- Centralized management of enterprise accounts: An enterprise can invite multiple accounts to join an organization and group the accounts by level based on the management or working structure of the enterprise.
- Centralized control of actions that each account can perform: The administrator of an organization can use service control policies (SCPs) to limit the permissions that can be assigned to an organization or the OUs in an organization. In the SCPs, you can limit which cloud services and APIs the member accounts in the organization can access.
- Integration with other Huawei Cloud services: The Organizations service integrates with other Huawei Cloud services (trusted services) to enable users to perform organization-wide operations.
Prerequisites
An organization has been created, and an account has been invited to join the organization. For details, see Creating an Organization and Inviting an Account to Join Your Organization.
Constraints and Limitations
Only the organization administrator and delegated administrators can manage permissions by organization.
An organization administrator is an account used to create an organization. An organization has only one organization administrator.
For more information about delegated administrators, see Delegated Administrator.
Procedure
- Log in to the SecMaster console.
- In the navigation pane on the left, choose Workspaces > Management. Figure 2 Accessing the Workspaces page
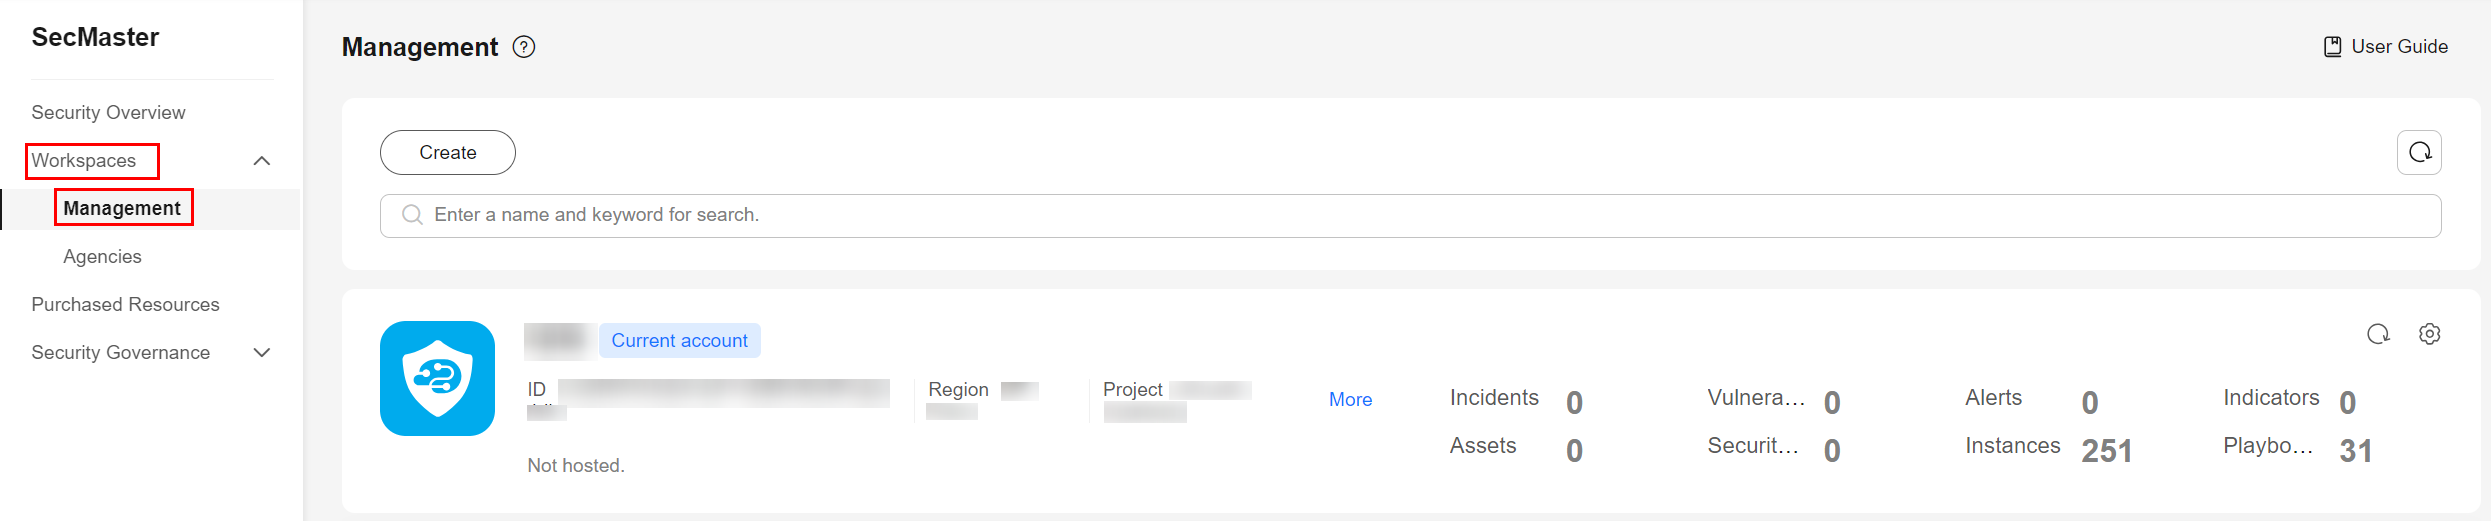
- On the workspace management page, click Service Authorization - Organization next to .
- On the displayed Service Authorization - Organization pane, select the organizations to be authorized and select Agree to authorize.
- Click Confirm.
What is your overall rating for this page?
Thank you very much for your feedback. We will continue working to improve the documentation.See the reply and handling status in My Cloud VOC.
For any further questions, feel free to contact us through the chatbot.
Chatbot


